
Anthropic has identified a significant escalation in the use of generative AI to automate romance scams, reporting in its September 2026 Threat Intelligence report that threat actors are now leveraging large language models to scale social engineering campaigns. These networks utilize AI-driven “fake dating apps” to bypass traditional security filters, signaling a shift from manual “pig butchering” factories toward fully autonomous social engineering agents.
The industrialization of these scams allows operators to maintain hundreds of simultaneous, intimate conversations with victims. Unlike previous iterations of romance fraud that relied on human operators in Southeast Asian call centers, these new systems use AI models to generate high-context, emotionally manipulative dialogue. This automation removes the human bottleneck, allowing scams to persist 24/7 without the overhead of a manual workforce.
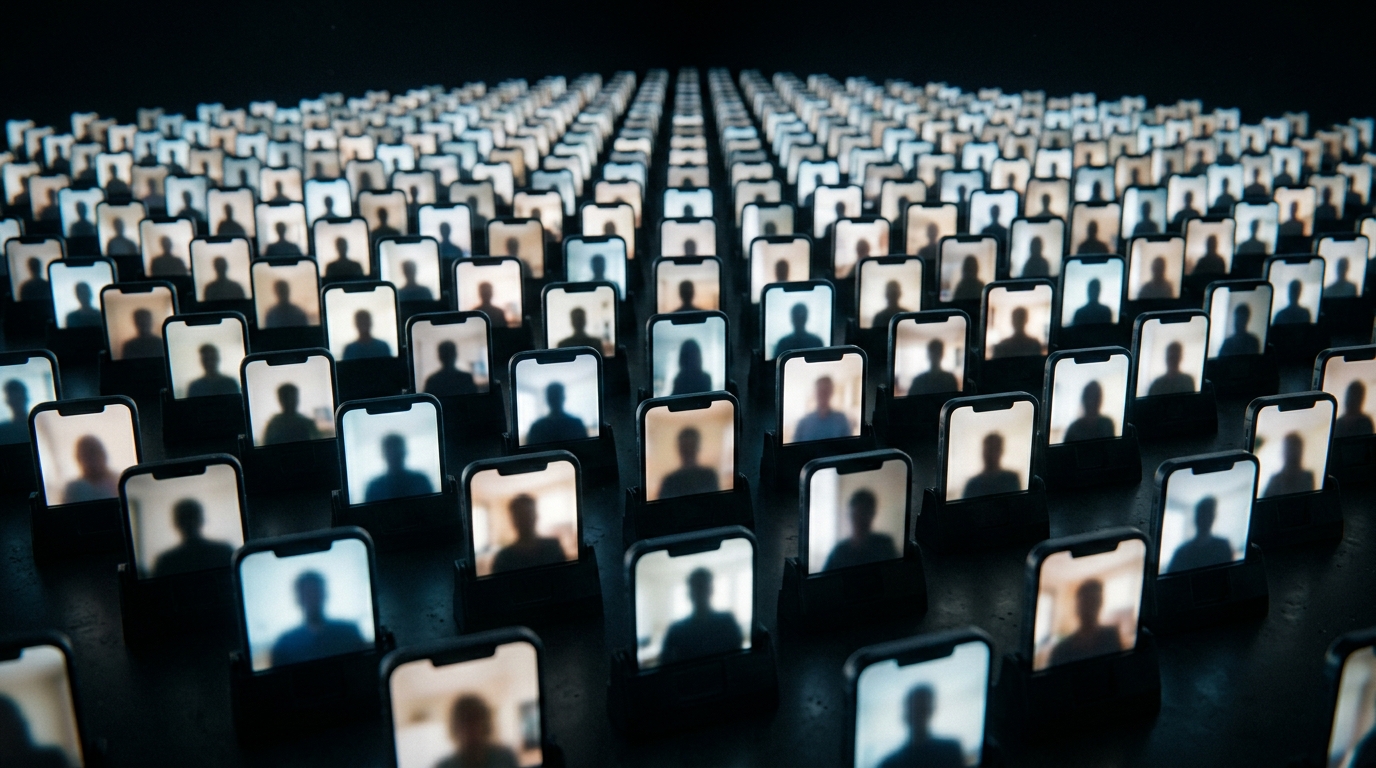
A critical component of this new era of fraud is the erosion of “video verification” as a reliable safety check. According to the 2026 Identity Fraud Report, deepfakes and synthetic media now account for approximately 20% of all biometric fraud attempts. This makes it increasingly difficult for users to distinguish between a genuine person and a synthetic persona during a brief or low-resolution call.
Security analysis suggests that while these AI agents are becoming more sophisticated, they still exhibit technical “hallucinations” and scripted rigidities. Research into these fraudulent platforms has highlighted instances where automated bots proceed with pre-programmed scripts regardless of the user’s input.
The financial impact of these scaled operations is substantial. The integration of AI-driven automation is projected to drive losses higher as the barrier to entry for threat actors drops. These automated agents are capable of “sensing” the psychological state of a victim through text analysis, adjusting their tactics in real-time to maximize the chances of financial extraction.
As synthetic intimacy becomes a primary tool for fraud, digital safety checklists that rely on “seeing a face” or “hearing a voice” are becoming obsolete. Practical mitigation now requires a focus on behavioral red flags—such as a persistent refusal to meet in person or immediate requests for financial transfers—rather than technical verification, which can now be simulated with high fidelity by malicious AI networks.
